Try segregation of duties, SailPoint, or Oracle ERP Cloud access review.
Federated IGA
Federated Identity Governance and Administration
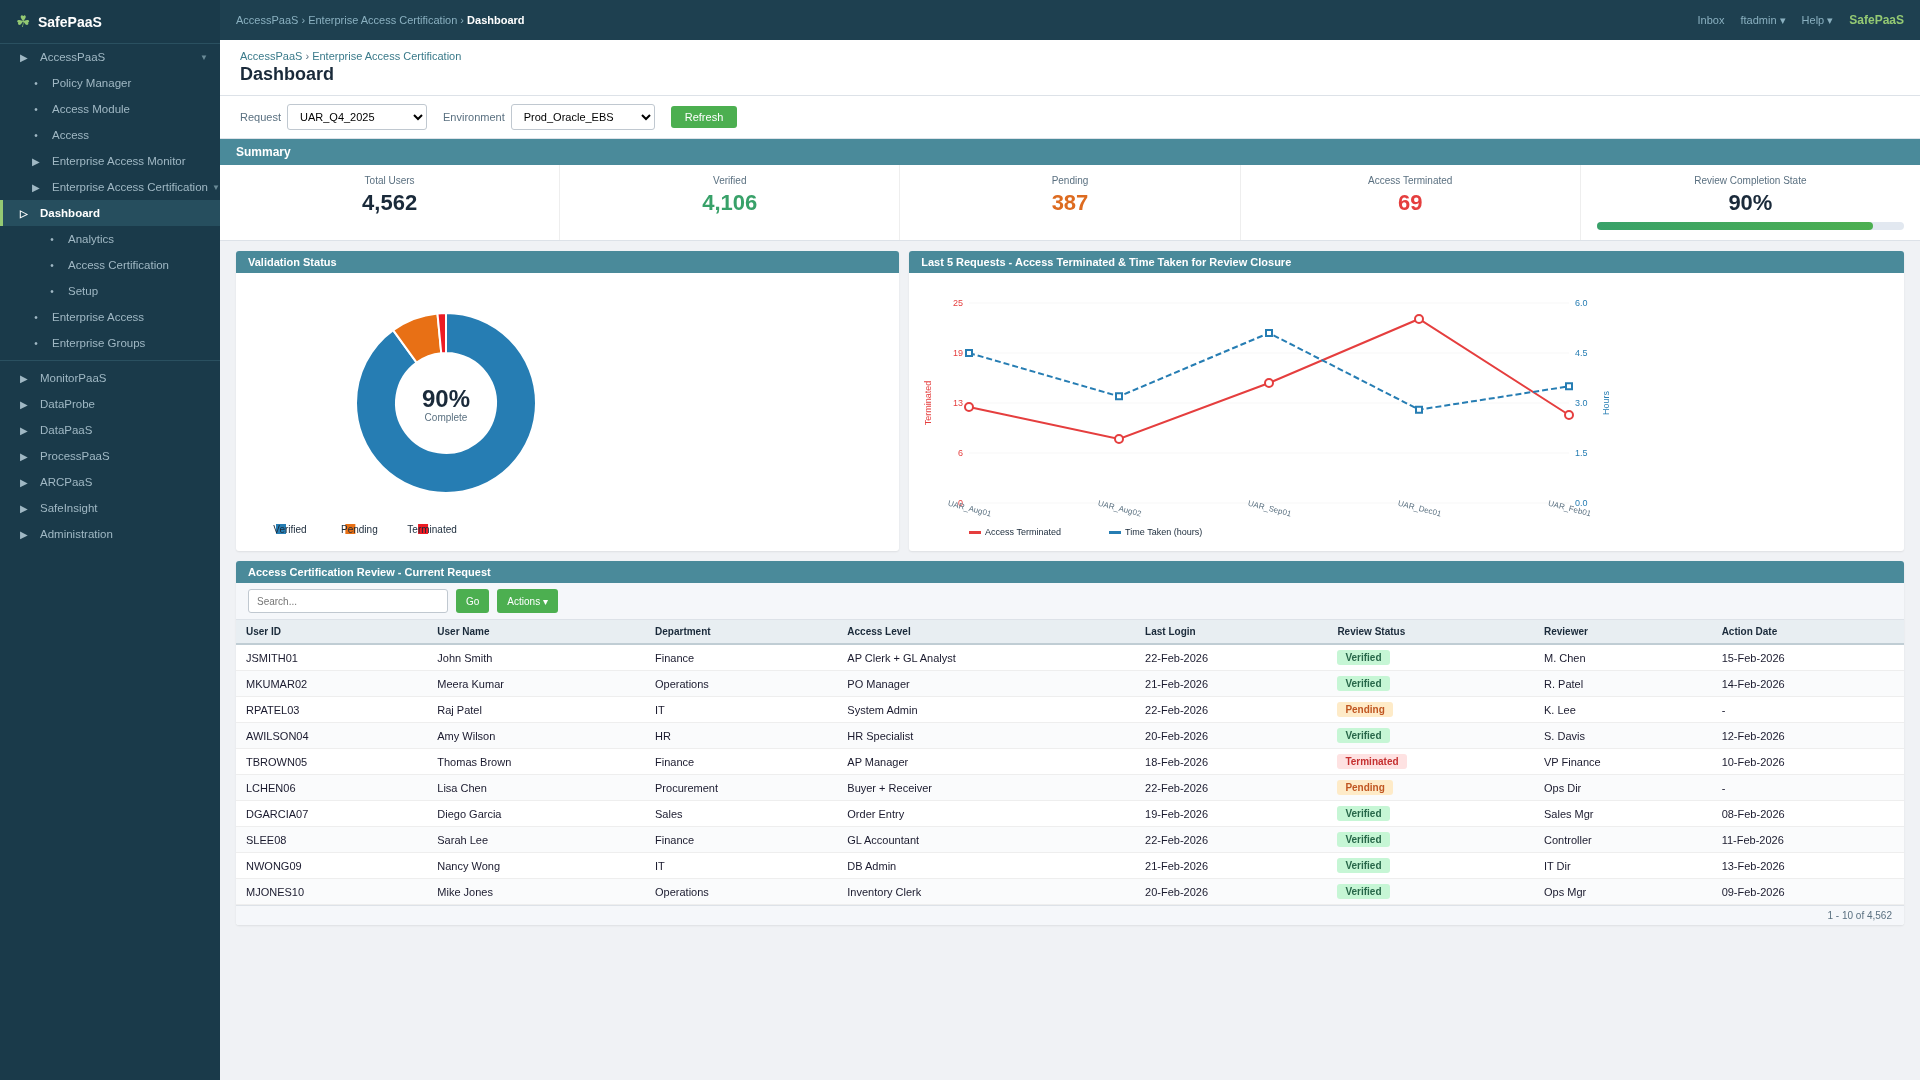
Identity Risk Exposure
80%
1 in 4
99%
$4.7M
Why Centralized Identity Governance Administration Matters
The Problem
- Fragmented systems, broken manual workflows.
Static models, disconnected tools, and manual processes leave toxic, excessive, and dormant access across critical systems.
The SafePaaS Solution
- Single federated governance layer.
SafePaaS adds one federated governance layer that standardizes policies, decisions, and evidence across SaaS, cloud, and hybrid environments.
All identities human and non-human from employees to AI agents, bots, service accounts, and API keys are governed together so that access always aligns with policy and business risk.Matters
Proven Impact: Real-World Business Outcomes
SafePaaS delivers quantifiable results across security, compliance, operations, and business enablement.
01
Up to 85% faster onboarding when SafePaaS automates identity lifecycle, approvals, and provisioning end-to-end across systems.
02
Up to 96% reduction in admin effort by replacing spreadsheet- and ticket-based access reviews with an automated solution
03
Up to 87% reduction in helpdesk & approval effort by using SafePaaS self-service, policy-driven workflows for routine access changes.
04
200–400% ROI in year one when organizations replace fragmented, manual access tasks with SafePaaS centralized identity governance.
How SafePaaS Sustains Results
SafePaaS combines federated governance, automation, and continuous monitoring so improvements are sustained—not one-time cleanups.
1
Governance Layer
2
Policy Automation
3
Continuous Monitoring
What Makes SafePaaS Unique
Unlike traditional IGA tools that bolt governance onto fragmented systems, SafePaaS was built as a federated governance layer that unifies humans and non‑human identities with embedded best practices, high‑touch delivery, and ongoing customer success.
Access Reviews & Certifications
Governed provisioning and lifecycle management
Role mining and role management
Audit‑ready analytics and reporting
Segregation of duties controls
Impact and materialized‑risk analysis
Privileged and host access governance
Non-Human Identity Governance
Policy‑driven automation and delegated administration
Business drivers and pains SafePaaS removes
| Pain Points | Problems Solved by SafePaaS |
|---|---|
| Security & risk | Excessive, toxic, dormant, and unmanaged access for human and non-human identities across critical systems. |
| Compliance | Pressure before audits, weak or scattered evidence, and inconsistent identity data across apps and environments. |
| Operational efficiency | Manual onboarding, access changes, and reviews that consume weeks of IT, security, and business-owner time. |
| Business enablement | Slow time-to-access for new hires, projects, AI agents, and partners, delaying value and innovation. |