Try segregation of duties, SailPoint, or Oracle ERP Cloud access review.
Identity and Access Management
Identity and Access Management
SafePaaS Identity and Access Management (IAM) is your identity control plane, centralizing all human and non‑human identities so every access decision follows least privilege, policy, and business risk. In a world where identity‑based attacks drive most incidents, IAM is your frontline defense.
All identities. Any application. Any environment.
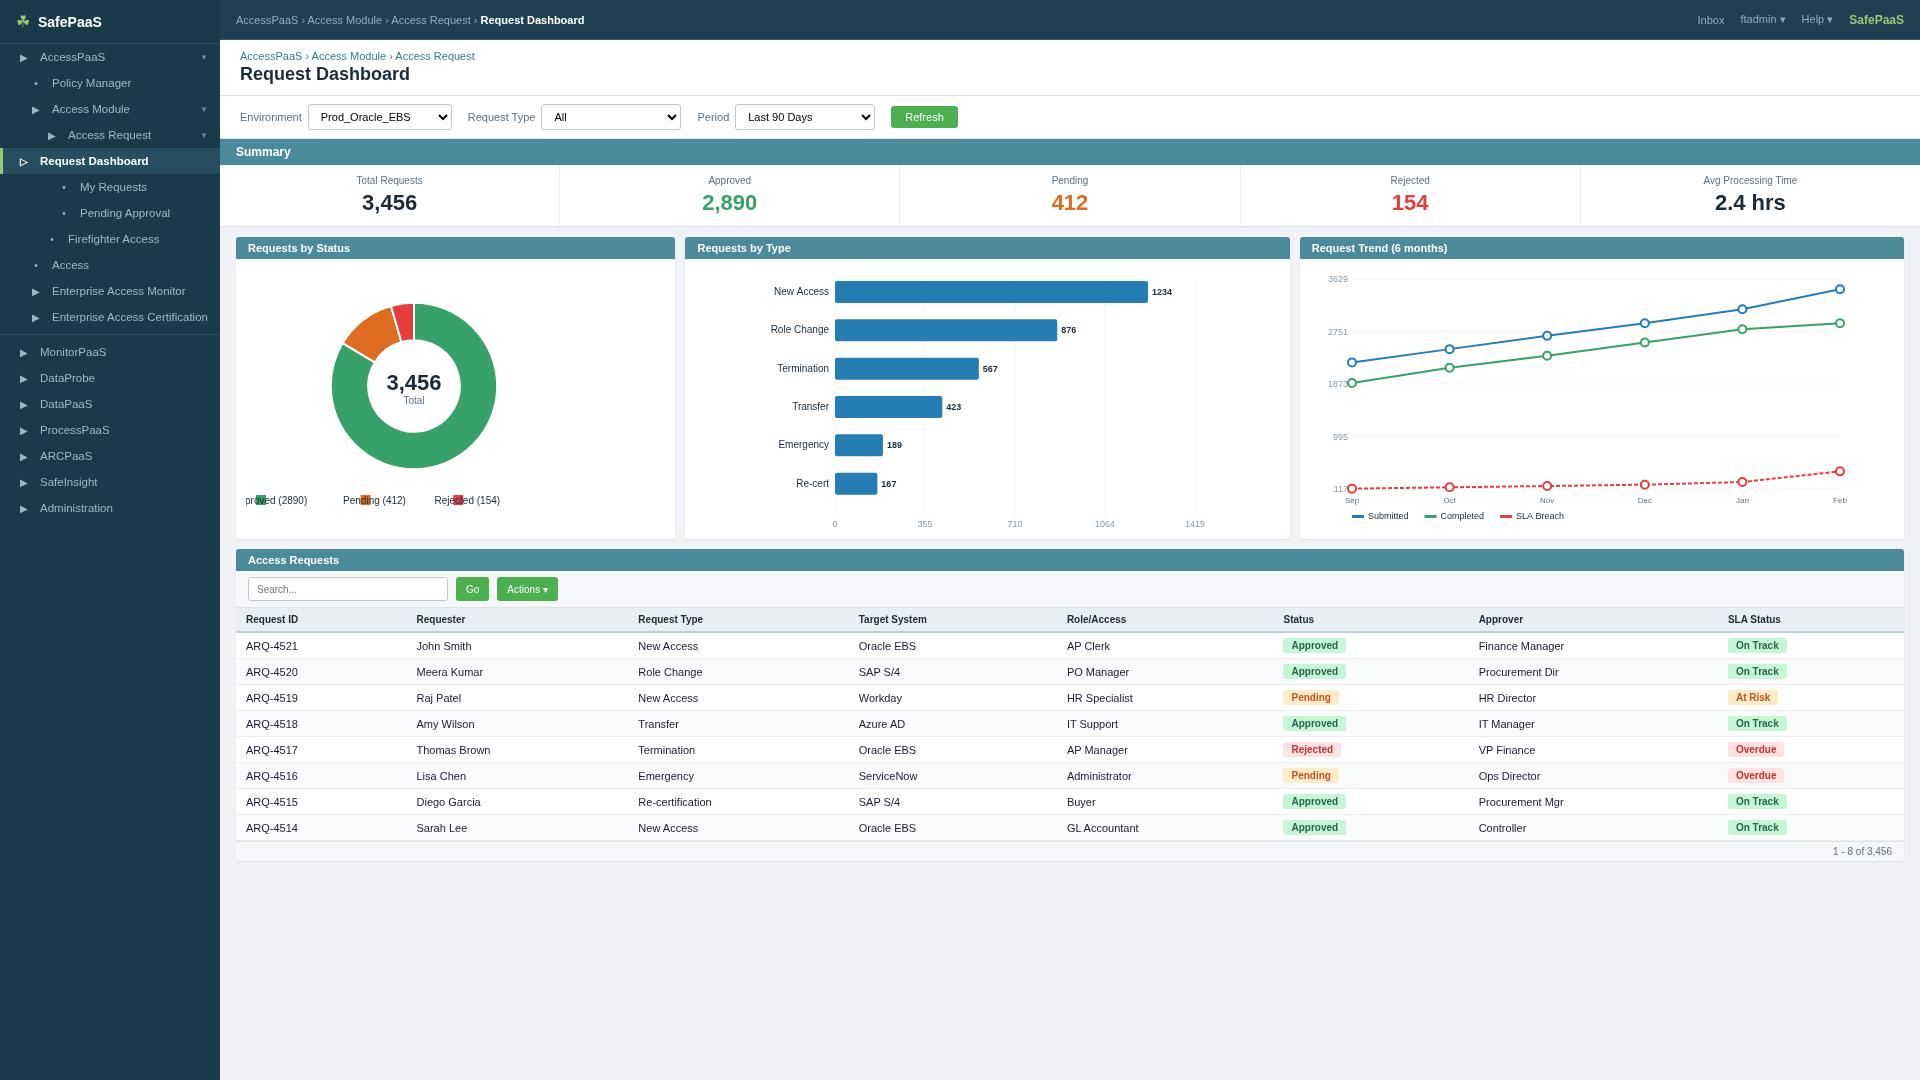
Proven impact for SafePaaS customers
1
40–60% less effort for provisioning and de‑provisioning by orchestrating joiner/mover/leaver workflows from one control plane.
2
3
Why modern IAM now
- Materially reduce identity risk and strengthen overall security posture with centralized, fine‑grained policy enforcement—essential as up to 86% of breaches now involve credential theft or misuse.
- Accelerate onboarding and change by replacing ticket‑driven workflows—enterprises currently take an average of six days to grant new hires full access to critical applications, creating avoidable security and productivity risk.
- Automate high‑volume identity tasks (reviews, SoD checks, provisioning) to free operations teams for higher‑value work, with customers often cutting provisioning effort by 40–60% through a single control plane.
How SafePaaS customers drive value with IAM
22%
Most major breaches now start with stolen or misused credentials rather than zero‑day exploits—stolen credentials are the top initial access vector in recent breach reports (around 22% of breaches).
79%
Attackers increasingly abuse valid accounts and permissions, with up to 79% of web application compromises tied to breached credentials and 56% of recent compromises linked to valid logins without MFA.
74%
Legacy IAM stacks, manual processes, and disconnected tools leave excessive, toxic, and dormant access across critical systems, contributing to 74% of breaches involving the abuse of privileged credentials.
Fortune 500 Insurance Company Modernizes Identity and Access Management with SafePaaS
A leading Fortune 500 insurance company leveraged SafePaaS IAM to modernize identity and access management across ERP, cloud, and legacy systems. By placing identity at the center of every access decision, the company reduced risk, streamlined compliance, improved operational efficiency, and accelerated business enablement. SafePaaS IAM ensures secure, policy-driven access for both human and non-human identities while enabling business agility.
Challenges
The company faced several identity and access management challenges:
01
- Excessive, dormant, or unmanaged access for human and non-human identities
- Difficulty enforcing least privilege and segregation of duties (SoD) at scale
- High likelihood of identity-driven breaches due to entitlement sprawl
02
- Pressure before audits and weak, scattered evidence of access activity
- Manual effort required to prove design and operating effectiveness for SOX and other mandates
03
- Manual onboarding, access changes, and reviews consumed weeks of IT, security, and business-owner time
- Repetitive access reviews and certifications were difficult to complete and interpret
04
- Slow time-to-access for new hires, projects, and partners delayed innovation
- Cloud and SaaS adoption slowed by access risk and compliance concerns
SafePaaS IAM Solution
01
- Detect and remediate risky entitlements and anomalous activity across critical applications
- Extend control to privileged users and sessions with time-bound, policy-aligned monitoring
02
- Orchestrate joiner, mover, and leaver events across ERP, cloud, and legacy systems from a single control plane
- Provision access on day one, check against policy and SoD rules, and revoke at exit to eliminate stale or orphaned accounts
- Empower business users with guided self-service access requests and approvals
03
- Replace static roles with dynamic, context-aware access policies across hybrid environments
- Use real-time signals—department, role, project, location—to grant, limit, or step up access
- Secure, frictionless access via SSO, federation, strong MFA, and risk-based policies
04
- Discover and inventory service accounts, APIs, and bots, bringing them under the same governance model as workforce identities
- Apply least privilege, automate lifecycle events, and prevent silent privilege creep
05
- Answer “who has access to what, why, and at what risk?” in seconds
- Detect SoD conflicts, excessive privileges, and policy violations continuously, not just at audit time
- Use role mining and insights to right-size roles and recommend safer entitlements
Business Impact
Security & Risk
Compliance
Operational Efficiency
Business Enablement
Driver-to-capability overview
| Driver | SafePaaS IAM capability |
|---|---|
| Security & risk | Centralized policies, least-privilege enforcement, SoD controls, and privileged access governance across human and non-human identities to reduce identity-driven incidents. |
| Compliance | Continuous access governance and evidence that answers “who has access to what, why, and at what risk?” for SOX and other key frameworks. |
| Operational efficiency | Automated joiner/mover/leaver, governed provisioning. |
| Business enablement | Fast, governed access for new hires, projects, partners, and services across SaaS, cloud, and ERP—supporting transformation without losing control. |